Pages

Wednesday, October 26, 2016

Cisco Free Lab Website - dCloud

Cisco dCloud has been moved to version 1.5 , now it is at version 2.

Cisco dCloud lab as a service platform provides self-service training, demonstration and lab capabilities for Cisco partners. Learn about this free 24/7/365 resource which provides multiple labs in all Cisco architectures, plus documentation and instructions for conducting on-site demonstrations. For anybody to sell/buy/use Cisco products, Cisco dCloud is a great place to practice configuring.
What DCloud does is give you the ability to test, demonstrate and run 131 different labs, demos and sandboxes.


Experience a Cisco solution in dCloud:
  • Browse to Cisco dCloud. Select the location closest to you and then log in using your Cisco.com credentials.


  • Find content. In the dCloud Catalog, search or filter to find content that best meets your needs. Open the content and then click Information to view additional details or Resources to view documentation and content guides.


  • Schedule a session. It may take 15 or more minutes after the scheduled start time for the session to become active.


  • Test your connection. Confirm that your network connection is fast enough to provide the best dCloud experience.

  • Access the session. Find your session in Dashboard > My sessions. Once the session is active, click the View button. Use a content guide to work through scripted scenarios, or explore the solution your own way.


  • Watch a Training Video. Get the most out of your dCloud experience by watching our short, overview video tutorials.


Access your scheduled session:

It may show 'starting' status for more than 10 minutes at the scheduled time after you logged into your dCloud account. 


Once it changed to 'View' status, you can click 'View' to access your lab. Your lab will be opened with a topology. In this example, you will see three n7k devices and one ad server, and one workstation. Click 'Resources' menu, you will get Lab Guide link for your this lab. It is a pdf file and will be opened from another browser window.


Click 'Servers' menu, it will list all devices information and server information. From wkst1, there is a 'Remote Desktop' link for you to open RDP session in a new browser window.


On this new RDP window, there is Putty shotcut on desktop. Three existing SSH sessions to N7K-1, N7K-2 and N7K-3 for you to open connections to three N7k devices.


login as: admin
User Access Verification
Password:
Cisco NX-OS Software
Copyright (c) 2002-2012, Cisco Systems, Inc. All rights reserved.
NX-OS/Titanium software ("NX-OS/Titanium Software") and related
documentation, files or other reference materials ("Documentation")
are the proprietary property and confidential information of Cisco
Systems, Inc. ("Cisco") and are protected, without limitation,
pursuant to United States and International copyright and trademark
laws in the applicable jurisdiction which provide civil and criminal
penalties for copying or distribution without Cisco's authorization.
The use of NX-OS/Titanium Software and Documentation is strictly
limited to Cisco's internal use.

Any use or disclosure, in whole or in part, of the NX-OS/Titanium
Software or Documentation to any third party for any purposes is
expressly prohibited except as otherwise authorized by Cisco in writing.
The copyrights to certain works contained herein are owned by other
third parties and are used and distributed under license. Some parts
of this software may be covered under the GNU Public License or the
GNU Lesser General Public License. A copy of each such license is
available at
http://www.gnu.org/licenses/gpl.html and
http://www.gnu.org/licenses/lgpl.html
n7k-2# show ver
Cisco Nexus Operating System (NX-OS) Software
TAC support: http://www.cisco.com/tac
Documents: http://www.cisco.com/en/US/products/ps9372/tsd_products_support_serie
s_home.html
Copyright (c) 2002-2012, Cisco Systems, Inc. All rights reserved.
The copyrights to certain works contained herein are owned by
other third parties and are used and distributed under license.
Some parts of this software are covered under the GNU Public
License. A copy of the license is available at
http://www.gnu.org/licenses/gpl.html.

Software
loader: version N/A
kickstart: version 6.1(2) [gdb]
system: version 6.1(2) [gdb]
kickstart image file is: bootflash:/titanium-d1-kickstart.6.1.2.gbin
kickstart compile time: 12/25/2020 12:00:00 [10/26/2012 04:25:57]
system image file is: bootflash:/titanium-d1.6.1.2.gbin
system compile time: 9/7/2012 13:00:00 [10/26/2012 05:25:42]


Hardware
cisco Nexus 7000 Unknown Chassis ("Unknown Module")
Intel(R) Xeon(R) CPU E7- 283 with 2066304 kB of memory.
Processor Board ID T5056BAE577

Device name: n7k-2
bootflash: 0 kB
Kernel uptime is 0 day(s), 0 hour(s), 23 minute(s), 12 second(s)


plugin
Core Plugin, Ethernet Plugin
n7k-2#


n7k-2# show run

!Command: show running-config
!Time: Thu Oct 27 01:06:31 2016

version 6.1(2)
license grace-period

hostname n7k-2
vdc n7k-2 id 1
limit-resource module-type m1 f1 m1xl m2xl
allocate interface Ethernet2/1-9
limit-resource vlan minimum 16 maximum 4094
limit-resource vrf minimum 2 maximum 4096
limit-resource port-channel minimum 0 maximum 768
limit-resource u4route-mem minimum 96 maximum 96
limit-resource u6route-mem minimum 24 maximum 24
limit-resource m4route-mem minimum 58 maximum 58
limit-resource m6route-mem minimum 8 maximum 8

feature telnet

username adminbackup password 5 ! role network-operator
username admin password 5 $1$jCPcWfz0$vAWNe70hz7omDHTFwffFt0 role network-admin
no password strength-check
ip domain-lookup
vlan dot1Q tag native
system default switchport
system jumbomtu 0
no logging event trunk-status enable
copp profile strict
snmp-server user admin auth md5 0x6d86012eb8219a8c68031c974492a8bc priv 0x6d86012eb8219a8c68031c974492a8bc localizedkey engineID 128:0:0:9:3:0:80:86:159:0:13
rmon event 1 log trap public description FATAL(1) owner PMON@FATAL
rmon event 2 log trap public description CRITICAL(2) owner PMON@CRITICAL
rmon event 3 log trap public description ERROR(3) owner PMON@ERROR
rmon event 4 log trap public description WARNING(4) owner PMON@WARNING
rmon event 5 log trap public description INFORMATION(5) owner PMON@INFO
snmp-server enable traps link

vrf context management
ip route 0.0.0.0/0 198.18.128.1
vlan 1

hardware forwarding unicast trace


interface Ethernet2/1
shutdown
no switchport
mac-address 0050.56ba.e522

interface Ethernet2/2
shutdown
no switchport
mac-address 0050.56ba.e523

interface Ethernet2/3
shutdown
no switchport
mac-address 0050.56ba.e525

interface Ethernet2/4
shutdown
no switchport
mac-address 0050.569f.0015

interface Ethernet2/5
shutdown
no switchport
mac-address 0050.569f.0015

interface Ethernet2/6
shutdown
no switchport
mac-address 0050.569f.0015

interface Ethernet2/7
shutdown
no switchport
mac-address 0050.569f.0015

interface Ethernet2/8
shutdown
no switchport
mac-address 0050.569f.0015

interface Ethernet2/9
shutdown
no switchport
mac-address 0050.569f.0015

interface mgmt0
ip address 198.18.133.222/18
line console
line vty
boot kickstart bootflash:/titanium-d1-kickstart.6.1.2.gbin
boot system bootflash:/titanium-d1.6.1.2.gbin
no system default switchport shutdown
n7k-2#
show ip int brie vrf ?
WORD VRF name (Max Size 32)
all Display all VRFs
default Known VRF name
management Known VRF name

n7k-2#
show ip int brie vrf all
IP Interface Status for VRF "default"(1)
Interface IP Address Interface Status

IP Interface Status for VRF "management"(2)
Interface IP Address Interface Status
mgmt0 198.18.133.222 protocol-up/link-up/admin-up


Juniper SRX340 HA Configuraiton

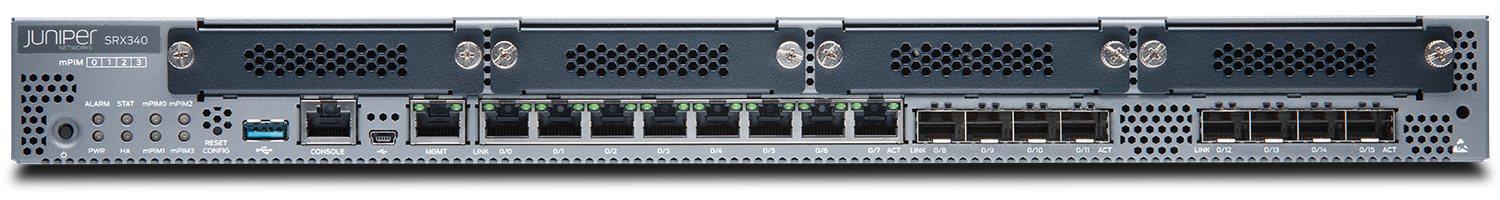
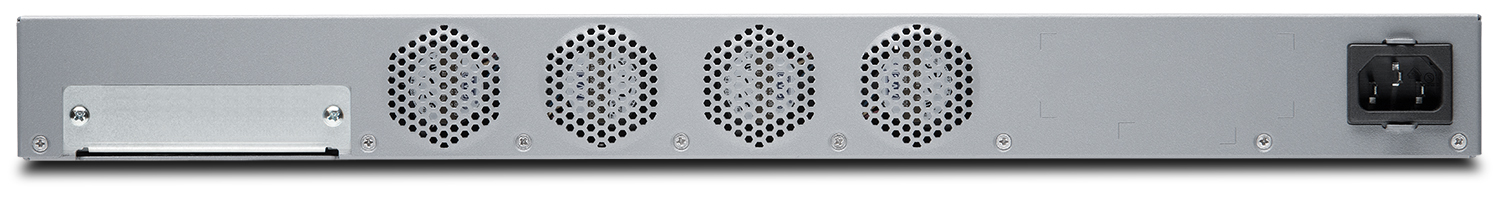
The SRX340 Services Gateway has a capacity of 3 gigabits per second (Gbps) and is 1 rack unit (U) tall. This services gateway has eight 1 G Ethernet ports, eight 1 G SFP ports, one management port, 4 GB of DRAM memory, 8 GB of flash memory, and four Mini-Physical Interface Module (Mini-PIM) slots.

SRX 340 Front Panel

SRX 340 Back Panel


The connection is a little different from SRX 240 and 1400. Here are some related posts:

Topology:


Configure Steps:
Chassis Cluster Flow Diagram (SRX300, SRX320, SRX340, SRX345, SRX550M, and SRX1500 Devices)


1. Remove Factory Default Configuration:

1.1 Factory Default Configuration
root> show configuration 
## Last commit: 2016-09-29 05:23:17 UTC by root
version 15.1X49-D45;
system {
autoinstallation {
delete-upon-commit; ## Deletes [system autoinstallation] upon change/commit
traceoptions {
level verbose;
flag {
all;
}
}
interfaces {
ge-0/0/0 {
bootp;
}
}
}
name-server {
208.67.222.222;
208.67.220.220;
}
services {
ssh;
telnet;
xnm-clear-text;
web-management {
http {
interface [ fxp0.0 ge-0/0/1.0 ge-0/0/2.0 ge-0/0/3.0 ge-0/0/4.0 ge-0/0/5.0 ge-0/0/6.0 ge-0/0/7.0 ];
}
https {
system-generated-certificate;
interface [ fxp0.0 ge-0/0/1.0 ge-0/0/2.0 ge-0/0/3.0 ge-0/0/4.0 ge-0/0/5.0 ge-0/0/6.0 ge-0/0/7.0 ];
}
}
dhcp {
pool 192.168.2.0/24 {
address-range low 192.168.2.2 high 192.168.2.254;
router {
192.168.2.1;
}
propagate-settings ge-0/0/0.0;
}
pool 192.168.3.0/24 {
address-range low 192.168.3.2 high 192.168.3.254;
router {
192.168.3.1;
}
propagate-settings ge-0/0/0.0;
}
pool 192.168.4.0/24 {
address-range low 192.168.4.2 high 192.168.4.254;
router {
192.168.4.1;
}
propagate-settings ge-0/0/0.0;
}
pool 192.168.5.0/24 {
address-range low 192.168.5.2 high 192.168.5.254;
router {
192.168.5.1;
}
propagate-settings ge-0/0/0.0;
}
pool 192.168.6.0/24 {
address-range low 192.168.6.2 high 192.168.6.254;
router {
192.168.6.1;
}
propagate-settings ge-0/0/0.0;
}
pool 192.168.7.0/24 {
address-range low 192.168.7.2 high 192.168.7.254;
router {
192.168.7.1;
}
propagate-settings ge-0/0/0.0;
}
pool 192.168.8.0/24 {
address-range low 192.168.8.2 high 192.168.8.254;
router {
192.168.8.1;
}
propagate-settings ge-0/0/0.0;
}
}
}
syslog {
archive size 100k files 3;
user * {
any emergency;
}
file messages {
any critical;
authorization info;
}
file interactive-commands {
interactive-commands error;
}
}
max-configurations-on-flash 5;
max-configuration-rollbacks 5;
license {
autoupdate {
url https://ae1.juniper.net/junos/key_retrieval;
}
}
## Warning: missing mandatory statement(s): 'root-authentication'
}
security {
screen {
ids-option untrust-screen {
icmp {
ping-death;
}
ip {
source-route-option;
tear-drop;
}
tcp {
syn-flood {
alarm-threshold 1024;
attack-threshold 200;
source-threshold 1024;
destination-threshold 2048;
timeout 20;
}
land;
}
}
}
nat {
source {
rule-set trust-to-untrust {
from zone trust;
to zone untrust;
rule source-nat-rule {
match {
source-address 0.0.0.0/0;
}
then {
source-nat {
interface;
}
}
}
}
}
}
policies {
from-zone trust to-zone trust {
policy trust-to-trust {
match {
source-address any;
destination-address any;
application any;
}
then {
permit;
}
}
}
from-zone trust to-zone untrust {
policy trust-to-untrust {
match {
source-address any;
destination-address any;
application any;
}
then {
permit;
}
}
}
}
zones {
security-zone trust {
host-inbound-traffic {
system-services {
all;
}
protocols {
all;
}
}
interfaces {
ge-0/0/1.0;
ge-0/0/2.0;
ge-0/0/3.0;
ge-0/0/4.0;
ge-0/0/5.0;
ge-0/0/6.0;
ge-0/0/7.0;
}
}
security-zone untrust {
screen untrust-screen;
interfaces {
ge-0/0/0.0 {
host-inbound-traffic {
system-services {
dhcp;
tftp;
}
}
}
}
}
}
}
interfaces {
ge-0/0/0 {
unit 0;
}
ge-0/0/1 {
unit 0 {
family inet {
address 192.168.2.1/24;
}
}
}
ge-0/0/2 {
unit 0 {
family inet {
address 192.168.3.1/24;
}
}
}
ge-0/0/3 {
unit 0 {
family inet {
address 192.168.4.1/24;
}
}
}
ge-0/0/4 {
unit 0 {
family inet {
address 192.168.5.1/24;
}
}
}
ge-0/0/5 {
unit 0 {
family inet {
address 192.168.6.1/24;
}
}
}
ge-0/0/6 {
unit 0 {
family inet {
address 192.168.7.1/24;
}
}
}
ge-0/0/7 {
unit 0 {
family inet {
address 192.168.8.1/24;
}
}
}
ge-0/0/8 {
unit 0;
}
ge-0/0/9 {
unit 0;
}
ge-0/0/10 {
unit 0;
}
ge-0/0/11 {
unit 0;
}
ge-0/0/12 {
unit 0;
}
ge-0/0/13 {
unit 0;
}
ge-0/0/14 {
unit 0;
}
ge-0/0/15 {
unit 0;
}
fxp0 {
unit 0 {
family inet {
address 192.168.1.1/24;
}
}
}
}

root>


1.2 Delete all default configuraiton

root> configure 
Entering configuration mode
The configuration has been changed but not committed

[edit]
root#
delete
This will delete the entire configuration
Delete everything under this level? [yes,no] (no) yes


[edit]
root#
set system root-authentication plain-text-password
New password:
Retype new password:

[edit]
root#
commit
Oct 4 03:42:44 init: dhcp (PID 1684) exited with status=0 Normal Exit
Oct 4 03:42:44 init: autoinstallation (PID 1682) exited with status=0 Normal Exit
commit complete

[edit]
root#


2. Enable Chassis Cluster on Node0 and Node1


[edit]
root#
show
## Last changed: 2016-10-04 03:42:37 UTC
version 15.1X49-D45;
system {
root-authentication {
encrypted-password "$5$kUxAKKC3$v6GLhluBqbu1.oksOHHLstkMNiG1hzCWtL9uhKEKfB1"; ## SECRET-DATA
}
}

[edit]
root# exit
Exiting configuration mode

root>
set chassis cluster cluster-id 9 node 0 reboot
Successfully enabled chassis cluster. Going to reboot now.

root>
*** FINAL System shutdown message from root@ ***

System going down IMMEDIATELY
                                                                               
OWaiting (max 60 seconds) for system process `vnlru' to stop...done
Waiting (max 60 seconds) for system process `vnlru_mem' to stop...done
Waiting (max 60 seconds) for system process `bufdaemon' to stop...done
Waiting (max 60 seconds) for system process `syncer' to stop...
Syncing disks, vnodes remaining...0 0 0 done

syncing disks... Syncing disks, buffers remaining... 12 12 12 11 11 7 7 7 7 7 7 7 4 4 4 4 4 4 4 3 3 3 3 3 3 3
Final sync complete
Uptime: 4d22h25m46s
Rebooting...
cpu_reset: Stopping other CPUs


SPI stage 1 bootloader (Build time: May 3 2016 - 23:48:30)
early_board_init: Board type: SRX_340

U-Boot 2013.07-JNPR-3.1 (Build time: May 03 2016 - 23:48:31)

SRX_340 board revision major:1, minor:7, serial #: CY3216AF0293
OCTEON CN7130-AAP pass 1.2, Core clock: 1200 MHz, IO clock: 600 MHz, DDR clock: 667 MHz (1334 Mhz DDR)
Base DRAM address used by u-boot: 0x10fc00000, size: 0x400000
DRAM: 4 GiB
Clearing DRAM...... done
Using default environment

SF: Detected MX25L6405D with page size 256 Bytes, erase size 64 KiB, total 8 MiB
Found valid SPI bootloader at offset: 0x90000, size: 1481840 bytes


U-Boot 2013.07-JNPR-3.1 (Build time: May 03 2016 - 23:50:19)

Using DRAM size from environment: 4096 MBytes
checkboard siege
SATA0: not available
SATA1: not available
SATA BIST STATUS = 0x0
SRX_340 board revision major:1, minor:7, serial #: CY3216AF0293
OCTEON CN7130-AAP pass 1.2, Core clock: 1200 MHz, IO clock: 600 MHz, DDR clock: 667 MHz (1334 Mhz DDR)
Base DRAM address used by u-boot: 0x10f000000, size:
.......<Omitted>
.
kern.securelevel: -1 -> 1
hw.re.gres_sync_other: 1 -> 0
Creating JAIL MFS partition...
JAIL MFS partition created
Boot media /dev/da0 has dual root support
** /dev/da0s2a
FILE SYSTEM CLEAN; SKIPPING CHECKS
clean, 1152837 free (53 frags, 144098 blocks, 0.0% fragmentation)
Tue Oct 4 03:49:59 UTC 2016
OOOOOOOOOOOOO
Amnesiac (ttyu0)

login: root
Password:

--- JUNOS 15.1X49-D45 built 2016-04-25 07:29:58 UTC
root@% 

note: Please make sure your cluster id is different if you are using multiple clusters in same network.

Verify Cluster Status after reboot.
{primary:node0}[edit]
root#
run show chassis cluster status
Monitor Failure codes:
CS Cold Sync monitoring FL Fabric Connection monitoring
GR GRES monitoring HW Hardware monitoring
IF Interface monitoring IP IP monitoring
LB Loopback monitoring MB Mbuf monitoring
NH Nexthop monitoring NP NPC monitoring
SP SPU monitoring SM Schedule monitoring
CF Config Sync monitoring

Cluster ID:
9
Node Priority Status Preempt Manual Monitor-failures

Redundancy group: 0 , Failover count: 1
node0 1 primary no no None
node1 0 secondary no no CF


Enable Cluster on Second Node, node1

root@%
cli

root>

root>

root>

root>

root>
configure
Entering configuration mode

[edit]
root#
delete
This will delete the entire configuration
Delete everything under this level? [yes,no] (no) yes


[edit]
root# set system root-authentication plain-text-password
New password:
Retype new password:

[edit]
root#
commit and-quit
commit complete
Exiting configuration mode

root> Oct 13 22:56:58 init: mountd-service (PID 20972) exited with status=1
Oct 13 22:56:59 init: exec_command: /usr/sbin/mountd (PID 20985) started
Oct 13 22:56:59 init: mountd-service (PID 20985) started
Oct 13 22:56:59 init: gstatd (PID 20973) exited with status=1
Oct 13 22:56:59 init: exec_command: /usr/sbin/gstatd (PID 20994) started
Oct 13 22:56:59 init: gstatd (PID 20994) started

root>
set chassis cluster cluster-id 9 node 1 reboot
Successfully enabled chassis cluster. Going to reboot now.


3. Basic Interfaces, Security Zones, Routes and Policies Configuration

{primary:node0}[edit]
set groups node0 system host-name fw-HA-1
set groups node0 interfaces fxp0 unit 0 family inet address 10.8.1.19/24
set groups node0 interfaces fxp0 unit 0 family inet address 10.8.1.21/24 master-only
set groups node1 system host-name fw-com-twn1-2
set groups node1 interfaces fxp0 unit 0 family inet address 10.8.1.20/24
set groups node1 interfaces fxp0 unit 0 family inet address 10.8.1.21/24 master-only
set apply-groups "${node}"
set chassis cluster reth-count 2
set chassis cluster redundancy-group 0 node 0 priority 200
set chassis cluster redundancy-group 0 node 1 priority 100
set chassis cluster redundancy-group 1 node 0 priority 200
set chassis cluster redundancy-group 1 node 1 priority 100
set interfaces fab0 fabric-options member-interfaces ge-0/0/3
set interfaces fab1 fabric-options member-interfaces ge-5/0/3
set interfaces ge-0/0/0 gigether-options redundant-parent reth0
set interfaces ge-5/0/0 gigether-options redundant-parent reth0
set interfaces ge-0/0/2 gigether-options redundant-parent reth1
set interfaces ge-5/0/2 gigether-options redundant-parent reth1
set interfaces reth0 redundant-ether-options redundancy-group 1
set interfaces reth1 redundant-ether-options redundancy-group 1
set security zones security-zone Zone1
set security zones security-zone Zone2
set security zones security-zone Zone1 host-inbound-traffic system-services all
set security zones security-zone Zone2 host-inbound-traffic system-services all
set interfaces reth0 unit 0 family inet address 10.8.2.14/24
set security zones security-zone Zone1 interfaces reth0.0
set interfaces reth1 unit 0 family inet address 10.8.3.13/24
set security zones security-zone Zone2 interfaces reth1.0


set system backup-router destination 10.0.0.0/8 10.8.1.1
set routing-options static route 0.0.0.0/0 next-hop 10.8.1.1

set security policies from-zone Zone1 to-zone Zone2 policy allow_any match source-address any
set security policies from-zone Zone1 to-zone Zone2 policy allow_any match destination-address any
set security policies from-zone Zone1 to-zone Zone2 policy allow_any match application any
set security policies from-zone Zone1 to-zone Zone2 policy allow_any then permit
set security policies from-zone Zone2 to-zone Zone1 policy allow_any match source-address any
set security policies from-zone Zone2 to-zone Zone1 policy allow_any match destination-address any
set security policies from-zone Zone2 to-zone Zone1 policy allow_any match application any
set security policies from-zone Zone2 to-zone Zone1 policy allow_any then permit


set security zones security-zone Zone2 tcp-rst
set security zones security-zone Zone1 tcp-rst


{primary:node0}[edit]
root#
commit
node0:
configuration check succeeds
node1:
commit complete
Oct 4 04:11:18 init: mountd-service (PID 2418) exited with status=1
Oct 4 04:11:18 init: exec_command: /usr/sbin/mountd (PID 2423) started
Oct 4 04:11:18 init: mountd-service (PID 2423) started
Oct 4 04:11:18 init: gstatd (PID 2416) exited with status=1
Oct 4 04:11:18 init: exec_command: /usr/sbin/gstatd (PID 2427) started
Oct 4 04:11:18 init: gstatd (PID 2427) started
Oct 4 04:11:18 init: l2cpd-service (PID 2414) exited with status=0 Normal Exit
Oct 4 04:11:18 init: exec_command: /usr/sbin/l2cpd (PID 2430) started
Oct 4 04:11:18 init: l2cpd-service (PID 2430) started
node0:
commit complete

{primary:node0}[edit]
root@fw-HA-1#


4. More Configuration
4.1 group configuration

set groups node0 system backup-router 10.8.1.1
set groups node0 system backup-router destination 10.44.20.160/24
set groups node0 system services ssh max-sessions-per-connection 32
set groups node0 system syslog file default-log-messages any info
set groups node0 system syslog file default-log-messages match "(requested 'commit' operation)|(copying configuration to juniper.save)|(commit complete)|ifAdminStatus|(FRU power)|(FRU removal)|(FRU insertion)|(link UP)|transitioned|Transferred|transfer-file|(license add)|(license delete)|(package -X update)|(package -X delete)|(FRU Online)|(FRU Offline)|(plugged in)|(unplugged)|GRES"
set groups node0 system syslog file default-log-messages structured-data
set groups node0 interfaces fxp0 unit 0 family inet filter input restrict_ssh

set groups node1 system backup-router 10.8.1.1
set groups node1 system backup-router destination 10.44.20.160/24
set groups node1 system services ssh max-sessions-per-connection 32
set groups node1 system syslog file default-log-messages any info
set groups node1 system syslog file default-log-messages match "(requested 'commit' operation)|(copying configuration to juniper.save)|(commit complete)|ifAdminStatus|(FRU power)|(FRU removal)|(FRU insertion)|(link UP)|transitioned|Transferred|transfer-file|(license add)|(license delete)|(package -X update)|(package -X delete)|(FRU Online)|(FRU Offline)|(plugged in)|(unplugged)|GRES"
set groups node1 system syslog file default-log-messages structured-data
set groups node1 interfaces fxp0 unit 0 family inet filter input restrict_ssh
set apply-groups "${node}"

set firewall filter restrict_ssh term ssh-from-nsm from source-address 10.44.20.0/24
set firewall filter restrict_ssh term ssh-from-nsm from destination-address 10.8.1.19/24
set firewall filter restrict_ssh term ssh-from-nsm from destination-address 10.8.1.20/24
set firewall filter restrict_ssh term ssh-from-nsm from destination-address 10.8.1.21/24
set firewall filter restrict_ssh term ssh-from-nsm from destination-port 22
set firewall filter restrict_ssh term ssh-from-nsm then accept
set firewall filter restrict_ssh term block-all-ssh from destination-address 10.8.1.19/24
set firewall filter restrict_ssh term block-all-ssh from destination-address 10.8.1.20/24
set firewall filter restrict_ssh term block-all-ssh from destination-address 10.8.1.21/24
set firewall filter restrict_ssh term block-all-ssh from protocol tcp
set firewall filter restrict_ssh term block-all-ssh from destination-port 22
set firewall filter restrict_ssh term block-all-ssh then count bad-access
set firewall filter restrict_ssh term block-all-ssh then log
set firewall filter restrict_ssh term block-all-ssh then syslog
set firewall filter restrict_ssh term block-all-ssh then reject tcp-reset
set firewall filter restrict_ssh term default-permit then accept


4.2 SNMP Configuration
set snmp filter-duplicates
set snmp v3 usm local-engine user junosAES authentication-md5 authentication-key "$$KO.v7-Vb2ZDi4ojqm5F3SrlKxNbs2gJGre24JZkqP5QFnCp0BhyltpORSyKvWLx-ds2gJZjHlKJGUjq.hSyevL-VwoaUyls2oaiHtu0OcyX7-dwY0BEyevLXbs2oaUHkPF39q.z6/CB1-VbsoJjq5z3Dj0BREyrZUDHkP369pO16/0IEcle4aJZk."
set snmp v3 usm local-engine user junosAES privacy-aes128 privacy-key "9$bp2ZU.mTQ3624/Ctu1Idbwg4ZiHmPQFUDApuORE24oJHqfTz9Cu3nlKvWx7Ujiq.5n6ApBI3ntOBIcSwY24aUHkPfQFmPT39CB1EcyrWLxNdbYg7NqmfT3n/Ctp0IEhrvMXyrMX-dg4ZUjHP56/tB1h/9u1IhrlJGUji.z36AtO/9ev8Xbw24aGk."
set snmp v3 vacm security-to-group security-model usm security-name junosAES group readonly
set snmp v3 vacm access group readonly default-context-prefix security-model usm security-level privacy read-view view_all
set snmp engine-id local 4014
set snmp view view_all oid 1 include
set snmp client-list snmpclient 10.4.1.0/24


4.3 System , Routing-options and Routing-instance Configuration

set system backup-router 10.8.1.1
set system backup-router destination 10.0.0.0/8
set system time-zone UTC
set system login class sec-read-only permissions view-configuration
set system login class sec-read-only allow-commands show
set system login class sec-read-only deny-commands "(clear)|(file)|(file show)|(help)|(load)|(monitor)|(op)|(request)|(save)|(set)|(start)|(test)"
set system login class sec-read-only deny-configuration all
set system login class super-user-cust idle-timeout 10
set system login class super-user-cust permissions all
set system login user test uid 2001
set system login user test class super-user
set system login user test authentication encrypted-password "$1$2po2xsGc$BUVkMEQGCf9.2CH7FCSA/"
set system services ssh
set system services netconf ssh
set system syslog archive size 750k
set system syslog archive files 2
set system syslog user * any emergency
set system syslog host 10.8.128.42 any any
set system syslog file messages any critical
set system syslog file messages authorization info
set system syslog file messages explicit-priority
set system syslog file interactive-commands interactive-commands error
set system syslog file traffic-create any any
set system syslog file traffic-create match RT_FLOW_SESSION_CREATE
set system syslog file traffic-deny any any
set system syslog file traffic-deny match RT_FLOW_SESSION_DENY
set system max-configurations-on-flash 10
set system max-configuration-rollbacks 30
set system license autoupdate url https://ae1.juniper.net/junos/key_retrieval
set system ntp server 10.9.16.5
set system ntp server 10.44.4.27

set routing-options static route 0.0.0.0/0 next-hop 10.8.1.1

set routing-instances def-vr instance-type virtual-router
set routing-instances def-vr interface reth0.0
set routing-instances def-vr interface reth1.0
set routing-instances def-vr routing-options static route 0.0.0.0/0 next-hop 10.8.2.1


Reference:

Tuesday, October 25, 2016

FortiOS 5.4.1 IPSec Phase 2 for AutoConf-enabled Phase1 Issue

The Fortigate 60D and 100D were used to build IPSec tunnel between two sites since last year. The Firmware version is 5.2.4 build 668. I were planning to upgrade Fortigate 100D to 5.4.1. The upgrade process were smooth but IPsec tunnel got broken after upgrade.

Fortigate60D IPSec Tunnel Configuration:

Fortigate100D I{Sec Tunnel Configuration:


Unfortunately, the tunnel between 60D and 100D failed to build after upgrade process rebooted the 100D. Based on following troubleshooting commands on 100D device, we found 100D ignored IKE request from 60D because of missing Phase2 proposal configuration.

diag debug reset
diag vpn ike log-filter clear
diag vpn ike log-filter dst-addr4 10.94.32.8
diag debug console timestamp enable
diag debug application ike -1
diag debug enable


I tried to put phase 2 on 60D firewall. It shows there is already phase 2 auto configuration from phase 1.


FW-60D(p2) #
get
name : p2
phase1name :
use-natip : enable
selector-match : auto
proposal : aes128-sha1 aes256-sha1 3des-sha1 aes128-sha256 aes256-sha256 3des-sha256
pfs : enable
dhgrp : 14 5
replay : enable
keepalive : disable
auto-negotiate : disable
keylife-type : seconds
encapsulation : tunnel-mode
comments :
keylifeseconds : 43200

FW-60D (p2) #
set phase1name
<string> please input string value
f1-f2 phase1

FW-
60D (p2) # set phase1name f1-f2

FW-
60D (p2) # set selector-match
exact Match selectors exactly.
subset Match selectors by subset.
auto Use subset or exact match depending on selector address type.

FW-
60D (p2) # end
For autoconf-enabled phase1, a phase2 is already generated internally.
object set operator error, -5 discard the setting
Command fail. Return code -5


It seems 60D with firmware version 5.2.5 is still using auto-configured IPSec Phase2. But 100D has not had that configuration after upgrade to 5.4.1. Quickly I manually put phase 2 configuration in 100D, the tunnel is up right away.


It seems with newer Firmware version, FortiOS changed their default configuration on IPSec Phase 2. You will have to manually put phase 2 configuration into VPN.


Monday, October 24, 2016

Check Point Firewall USB Installation Step by Step (R77.20 and R77.30)

Customer is asking a new fresh installation on their UTM 272 devices and apparently usb stick or usb cd-rom is best solution. Checkpoint sk65205 explains very detail for all steps. I did follow the Check Point instruction but still got a problem while using USB stick. Here are all my steps I worked on.

1. Preparing USB Stick

I am using a Kingston Traveller G3 8G USB stick which shows supported from Check Point sk92423 (Which USB flash keys work with ISOmorphic Tool).

2. Use ISOMorphic to make a R77.20 bootable USB Stick.


3. Start your Device with USB Stick Plugged in

Insert USB Stick into one of two Check Point Appliance UTM 272 USB ports. Powered on device:

4. BIOS Configuration

Press TAB or DEL to enter into BIOS setup the booking devices. USB-HDD and USB-CDROM has been picked for boot devices.

5. USB Stick Does Not Work

Unfortunately the system did not start with the USB device but still with internal hard disk drive. I did find following error messages from the booting screen:

usb 1-2: device not accepting address 2, error 071

 6. USB CDROM Worked

No Matter how I did the configurations on appliance, usb still did not work. I gave up and tried another UTM272, but same result. Finally I got a USB CD-ROM, burned same image into a DVD, it was able to get me into SYSLINUX page.

 7. With those options, the only works is Smart-1 option. 

 8. Installing

After you entered Smart-1 option, the installation is completely automatic.

9. Complete Installation

Wait probably 15-30 minutes, the whole installation will be done and your console window will show your appliance can be safely rebooted with new image. Also Appliance LCD Screen will show ***Installed*** R77.20 124. Powers Cycle your device, you will get your a new fresh installed R77.20. By the way, first time installation wizard will be used to configure your device with LAN port ip set to 192.168.1.1. User name is admin and password is admin.


Notes:

I tested the stick with my laptop, and it is able to booted from USB stick and I did get SYSLINUX prompt on my laptop. It bothered me a couple of day why it is not working on UTM 272s.

Since USB CD-ROM is working, I decided to wipe USB Stick out and tried ISOMorphic again on another laptop. This time, USB Stick works. I am guessing when ISOMorphic is making a bootable USB Stick, your computer is going to affect the final image on the stick.

More notes on Oct 2016;
Tried it again on Check Point 2012 4200 appliance to install R77.30. I were using same usb memory stick as my previous post. Added some more screenshots and words here:

once you plugged in your usb key, if it has been recognized, you will get a chance to run setup or boot it from network.
You may get a error message to say usb 3-1: device descriptor read/all, error -71

If all goes well, you should get SYSLINUX 4.06 booting screen and choose serial as output:

starting installation process


Reference:


Gartner Magic Quadrant for Cloud-Enabled Managed Hosting, North America (2015, 2014)

Cloud-Enabled Managed Hosting Market Definition/Description

The cloud-enabled managed hosting (CEMH) market deals in standardized, productized hosting offerings that combine a cloud-enabled system infrastructure (CESI) platform — comprising compute, network and storage hardware owned and operated by a service provider — with cloud management platform software to facilitate self-service and rapid provisioning with managed services (see "Technology Overview for Cloud-Enabled System Infrastructure" note that this document has been archived; some of its content may not reflect current conditions ). The infrastructure platform may be located in a service provider's data center, or optionally at the customer's data center, but, either way, it requires standardized deployment across all customers and uses a single code base that has been pre-engineered and/or predeployed by the provider prior to customer sign-up. At minimum, a service provider must supply server OS management services, including guest OS instances when virtualization is used. The provider may optionally supply other managed and professional services relating to the infrastructure's deployment and operation.
Cloud-enabled managed hosting allows only limited customization. It is sold on a stand-alone basis, with no requirement to bundle it with — for example — application development, application maintenance or data center outsourcing (DCO) services.
Customers must be able to access a self-service interface, which may be different from the platform interfaces used internally by the provider. A service provider can potentially intervene in the self-service workflow to manually approve, deny or alter a customer's requests, as long as the provisioning requested is fulfilled in a fully automated manner thereafter. Managed services (such as OS backups, patching and monitoring) must be available to customers on commitments of less than one year.

For a more detailed overview of cloud-enabled managed hosting, see "Technology Overview for Cloud-Enabled Managed Hosting."
This Magic Quadrant focuses on the enterprise-class cloud-enabled managed hosting market. Multiple delivery models are used in this market:
  • Multitenant, on the provider's premises: Compute, storage and networking hardware is shared by many customers, housed in the service provider's facilities and fully managed by that provider. This is the most common use case. It encompasses cloud infrastructure as a service (IaaS) offerings for which the provider offers management of guest OS instances.
  • Single-tenant, on the provider's premises: Compute and storage hardware is dedicated to one customer and housed in the service provider's facilities.
  • Single-tenant, on the customer's premises: Compute, storage and networking hardware is dedicated to one customer and housed in that customer's data center facilities, but owned and managed by the service provider in a nearly identical fashion to the multitenant and single-tenant provider-housed approaches.
In addition to server OS management, managed and professional services related to infrastructure operations may be offered, such as:
  • Management of infrastructure software at the middleware or persistence layer, such as Web server software, application servers and database servers
  • Management of storage, including backup and recovery
  • Management of host-based and network-based security functions
  • Management of network devices, such as application delivery controllers
  • Professional services associated with hosting, such as architecture consultation, capacity planning, performance testing, security auditing and data center migration
Cloud-enabled managed hosting services must be available to customers on contracts shorter than the multiyear contracts historically used for traditional managed hosting. Customers may opt for longer contracts of one to three years to secure greater overall discounts, but this is entirely at their discretion. Ultimately, cloud-enabled managed hosting must afford customers the ability to change the amount of capacity in use without any contract alterations.
Use Cases Covered by This Evaluation
This Magic Quadrant focuses on the following common use cases, independent of the type or types of infrastructure used for the associated workloads:
  • E-business hosting for digital marketing sites, e-commerce websites, SaaS, social websites, and similar modern online properties and applications. These workloads are often complex and are associated with a high rate of change in systems and application infrastructure.
  • Web-based business application hosting for corporate intranets and Web-based applications delivered to users primarily within enterprises. The applications may be commercial software or developed in-house; workloads are often relatively static and do not have a high rate of change.
  • Enterprise application hosting. Managed hosting for the infrastructure used to support large commercial software applications, such as those of Oracle, SAP and other enterprise software vendors. These workloads are often complex and require specialized knowledge to operate optimally, but do not have a high rate of change.

In 2016, Gartner will be making a number of significant changes to Magic Quadrants related to the hosting and Infrastructure-as-a-Service markets, including the retirement of some Magic Quadrants into overall Market Guides, and the launch of a brand new Magic Quadrant.
In 2015, we noted in both our Magic Quadrant for Cloud Infrastructure as a Service, Worldwide and our Magic Quadrant for Cloud-Enabled Managed Hosting, North America the rather significant changes that were taking place in the market for hosting and cloud infrastructure services. Through thousands of inquiries with end-user organizations over 2014 and 2015, Gartner has watched as customers have evolved their view of the marketplace. The outsized mindshare that hyperscale Infrastructure-as-a-Service platforms such as Amazon Web Services, Microsoft Azure, or Google Compute Engine have obtained has led buyers to analyze these offerings as far more than a vendor or a technology … but as more of an overall “strategic platform” for their organizations to build new and innovative/disruptive applications on over the next decade. This is especially true among North American clients.
Therefore Gartner will be making the following changes to our Magic Quadrants in the hosting and IaaS markets in 2016:
  • First, Gartner will be launching a new “Magic Quadrant for Public Cloud Infrastructure Managed Service Providers, Global” in 2016. More details on this Magic Quadrant will be available soon on Lydia Leong’s blog.
  • Second, in order to make room for the new Magic Quadrant for Public Cloud Infrastructure Managed Service Providers, and because buyer behavior in North America has moved the most towards this direction, we have retired our Magic Quadrant for Cloud-Enabled Managed Hosting in North America. In its place, we will be publishing a North American Market Guide for hosting for our end-user clients, roughly at the same time last year’s Magic Quadrant was published (July).
  • Third, in Europe and Asia-Pacific there is still more of a focus on locally-hosted services than in North America, therefore our Magic Quadrants for Cloud-Enabled Managed Hosting will continue in those markets but will be changing their focus slightly, as represented by their new titles – Magic Quadrant for Managed Hybrid Cloud Hosting.


2015
Magic Quadrant for Cloud-Enabled Managed Hosting, North America, 2015
https://www.gartner.com/doc/reprints?id=1-2K50B8G&ct=150729&st=sb

2014
Gartner Magic Quadrants tend to evolve over time as technologies and buyer expectations mature, and our views on the hosting market are no exception.  Gartner has been publishing Magic Quadrants in the hosting market since 
2004 1998, which later became a combined hosting and cloud IaaS Magic Quadrant in 2009 (link) and now the two exist as separate Magic Quadrants.  The first thing that most readers will notice in this year’s MQ is the change in title –Cloud-Enabled Managed Hosting.

This is not simply a cloudwashing of our previous Magic Quadrant for Managed Hosting, the term Cloud-Enabled encapsulates how we view the market as evolving at this point in time.   In a nutshell, Gartner expects that Cloud-Enabled Managed Hosting will evolve managed services over the next several years … much like Infrastructure-as-a-Service has done to infrastructure provisioning and management over the past several years.

Why has the name of the Magic Quadrant for Managed Hosting changed to “Cloud-Enabled Managed Hosting”?
These new Magic Quadrants cover the market that is created by the intersection of managed services and a cloud-enabled infrastructure platform (which might or might not be cloud IaaS).  These magic quadrants will begin to place more focus more on the service layer on top of the infrastructure, rather than the infrastructure itself.

Magic Quadrant for Cloud-Enabled Managed Hosting, North America, 2014


http://blogs.gartner.com/douglas-toombs/the-2014-magic-quadrant-for-cloud-enabled-managed-hosting-in-north-america/

http://pages.peak10.com/%20Gartner-Magic-Quadrant-Landing-Page.html

http://www.peak10.com/wp-content/uploads/2015/04/2014-magic-quadrant-for-cloud-enabled-managed-hosting-north-america.pdf